Strategy to Run: the full arc, across your application estate
One partner accountable from the strategy to the systems running in production, so the governance and the record never break at a supplier seam. Delivered in phases, on one platform, with the evidence continuous from the first architecture decision to the applications in service.
Strategy to Run is the whole arc as one continuous engagement. We set the strategy and the target architecture with your leadership. We stand up FORGE inside your enterprise and enable your teams on it. We take your applications through it, deciding with you what to rebuild, what to reuse and what to retire, and we run what we deliver. Governance to production to support, on one platform, with one record running through it.
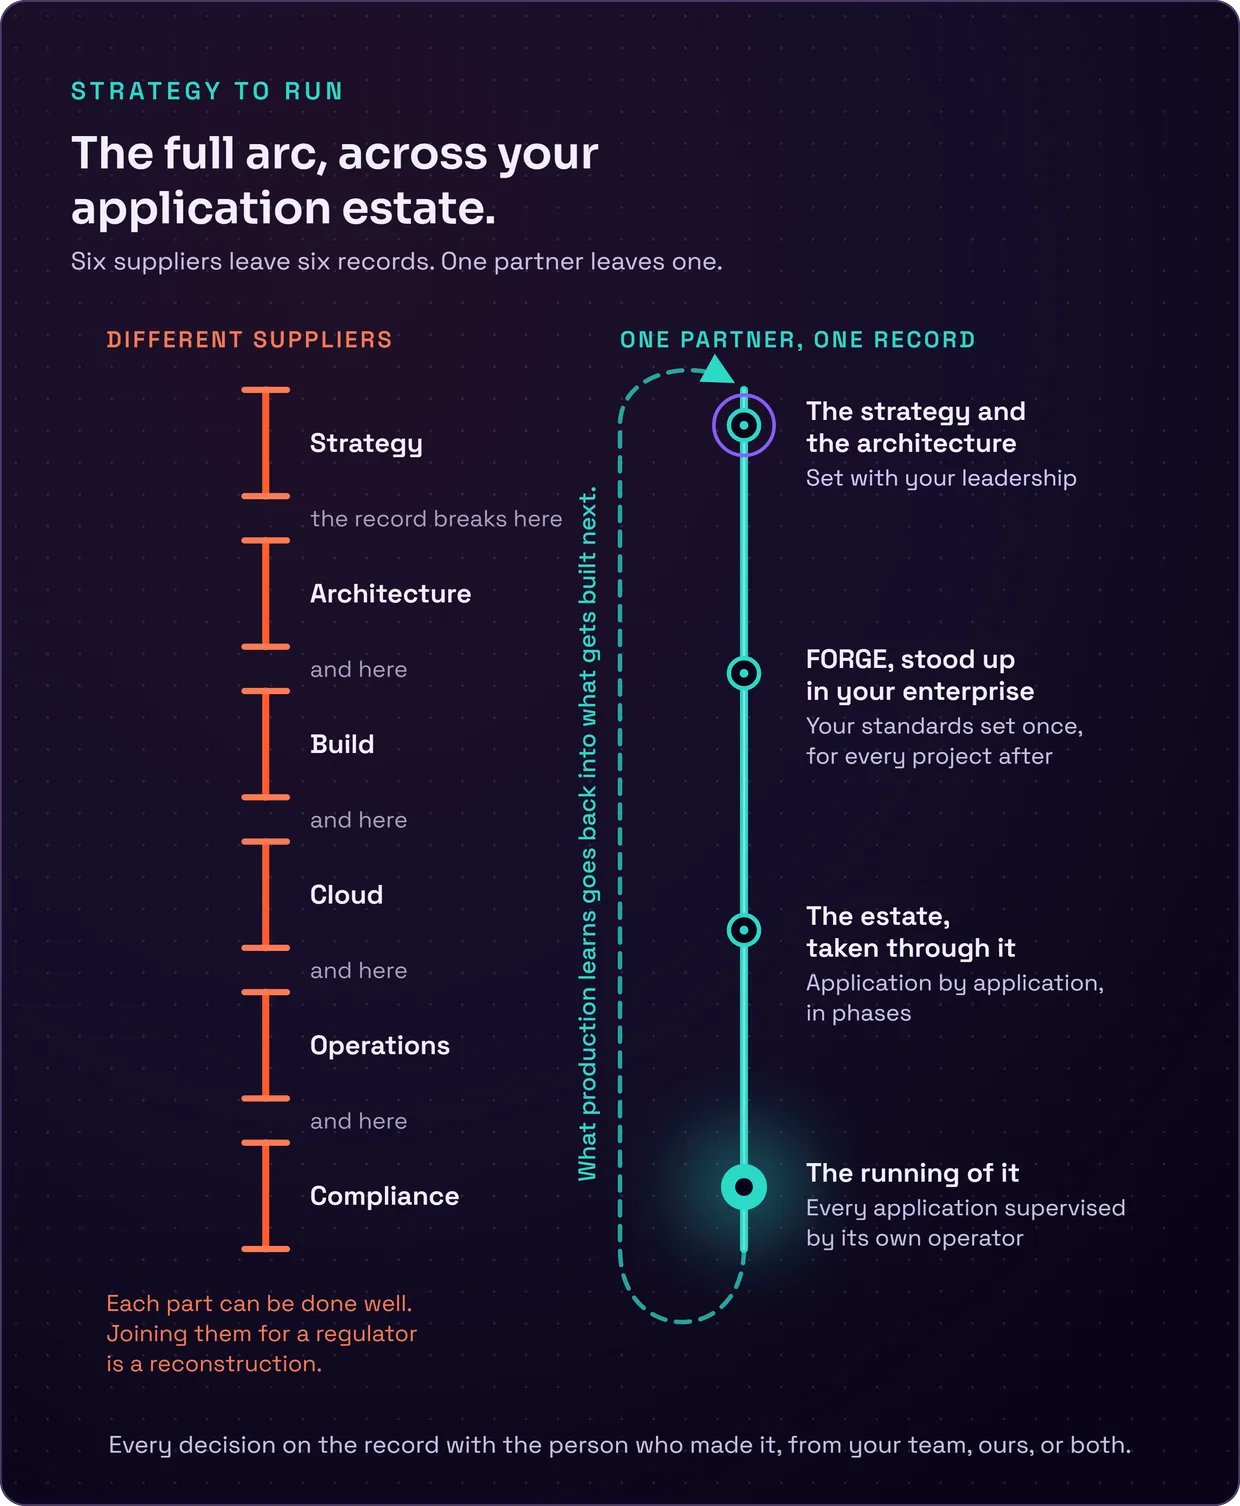
When strategy, architecture, build, cloud, operations and compliance come from different suppliers, each part can be done well. The record breaks at the handovers. The evidence of how a system was built lives in one place and the evidence of how it is run lives in another. Joining them for a regulator is a reconstruction, not a lookup. Strategy to Run runs the whole arc on one platform. The standards your architects and security engineers set once reach every application without them reviewing each one. Every project's pipeline is generated from your policy. Every cloud application arrives with its evidence and its own operator. Every decision along the way is on the record with the person who made it, from your team, ours, or both. The arc compounds as it runs. What one application learns in production goes back into the patterns the next one is built from. Nothing learned elsewhere acts on your system until it has been proven on your system. Each phase starts further along than the one before. The capability the programme stands up is yours and outlasts it.
What's included
One programme, four movements, on one platform.
- The strategy and the architecture. Where AI belongs in your business and where it does not. What to rebuild, what to reuse and what to retire, and the build-ready target architecture. What a system will cost to run is known before it is built and checked against the ceiling agreed at the start. The result is written down as the standards FORGE enforces on every build that follows.
- FORGE, stood up in your enterprise. Your standards, security controls and pipeline policy set once, for every project after. Your engineers and your business builders enabled on it and taught the discipline alongside the product, so the capability is yours, not rented.
- The estate, taken through it. Application by application, in phases. Rebuilt or re-engineered on the cloud your architects chose, through generated pipelines, on a governed data layer. Each arrives with its evidence and its own operator. Where a rebuild replaces a system you cannot afford to break, we recover what it does first. The old and the new then run side by side on real traffic until you are satisfied. Full DevSecOps deployment across AWS, Azure, Google Cloud (GCP) and Oracle Cloud (OCI), from the provider's own modules or from our labs.
- The running of it. Every cloud application supervised by its own operator, with BtSavvy's engineers taking the hard case themselves. Everything it does, and everything it declines to do, is on the record. Releasing code stays with people. Risk, security and AI governance as continuous, audit-ready evidence, produced as the work happens. For AI products in regulated markets, the record a regulator asks for is an output of the build.
Across the programme, one governance surface covers every application, business-built and engineer-built alike. FORGE shows which projects are behind your published standards, and before you change a standard you can see what the change would affect. A project that has fallen behind a standard is found at the moment of work, not at the audit. Commercial shape, phasing and team structure are scoped per programme and come out of the Diagnostic that precedes it.
When to engage
When the ambition spans the estate, and you are changing how the organisation builds and runs software.
The board has set an enterprise-wide AI mandate, and there is no delivery capability under it that anyone would stake the mandate on. The application portfolio needs rationalising, and the answer has to come with the means to carry it out. An earlier multi-supplier programme broke at the seams, and that is why one accountable partner is now the requirement. Regulatory posture requires one chain of accountability from the strategy to the running systems, and it cannot be reconstructed from disconnected supplier artefacts.
What comes next
Strategy to Run is the top of the ladder, so its next step is inside it. Each phase and each application under the programme starts further along than the one before. Each adds to the standards and the patterns everything later inherits. Any one of those parts can be bought on its own. What cannot be bought piecemeal is the loop: requirements, design, build, pipeline and production operation on one platform. What production learns goes back into what gets built next. The capability the programme stands up, the standards, the patterns and the enabled teams, is yours and outlasts the programme. A Diagnostic typically comes first, to scope the arc. A Proof or a First Build often precedes it as the working evidence the programme is scoped against.
Talk to us about Strategy to Run.
Strategy to Run begins with a conversation, usually following a Diagnostic. A BtSavvy engineer will scope it with your engineering leadership or business sponsor.